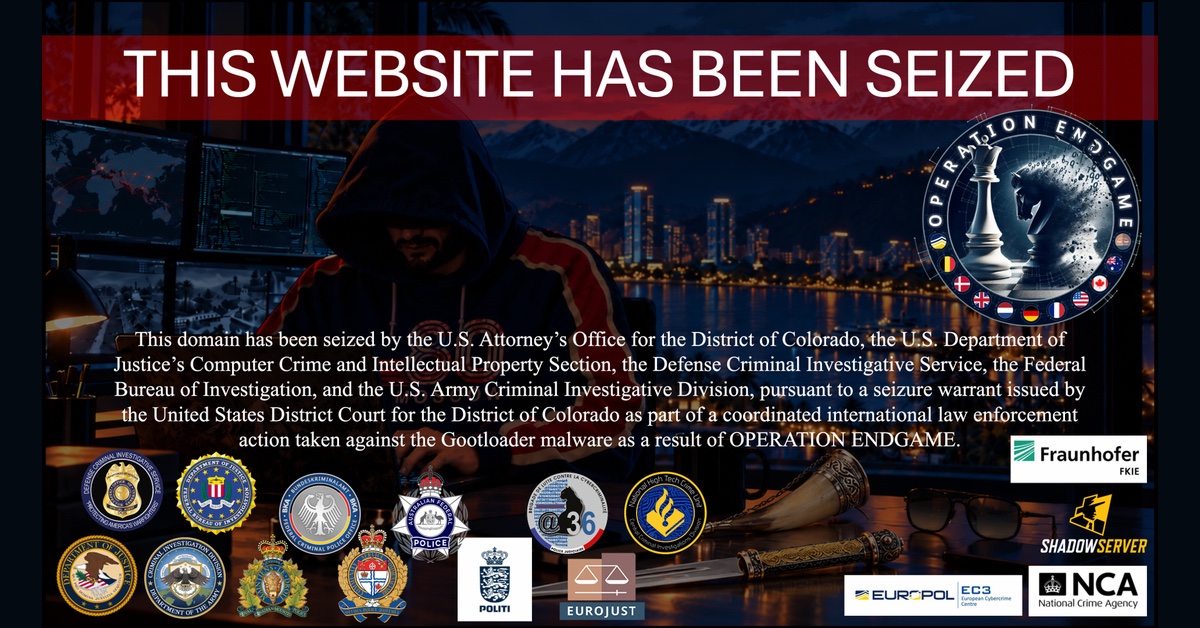
Authorities removed Gootloader malware from more than 100 servers and seized U.S. domain names used to spread and control it, the Justice Department announced Thursday.
The malware has infected at least 25,000 computers worldwide since 2018, according to the department. It linked Gootloader to ransomware attacks against at least 44 U.S. victims, with losses totaling about $28.8 million.
The court-authorized operation involved the FBI and international partners. Among the servers cleaned were those hosting compromised WordPress websites, the department said.
The figures and account of the disruption come from the Justice Department and have not been independently verified by Virginia Times.
How Gootloader Spread
Warrants unsealed this week describe a scheme that often began by deceiving someone into downloading the malware, according to the release. An infected computer then became part of a botnet — a network of compromised computers.
Gootloader’s operators used that network to infect additional computers and sold access to those machines to criminals who deploy ransomware, prosecutors said.
Kenneth DeChellis, special agent in charge of the Defense Criminal Investigative Service’s Cyber Field Office, said targets included the U.S. Department of War and the defense industrial base. The release did not identify individual victims or detail those attacks.
FBI Cyber Branch Operations Director Brett Leatherman said the disruption combined technical operations with efforts to notify victims and help them remove infections.
The Shadowserver Foundation worked with internet service providers and computer security incident response teams to locate infected systems, contact victims and support cleanup, according to the department. The Justice Department said visitors to the seized domains would see a law enforcement seizure notice.
International Investigation
The operation was conducted in coordination with Operation Endgame, an international effort aimed at disrupting malware services used by cybercriminals.
The FBI’s Denver Field Office, the Defense Criminal Investigative Service and the Army Criminal Investigation Division led the Gootloader investigation.
They worked with authorities in Germany, the Netherlands, Canada, Denmark, France, the United Kingdom and Australia, as well as Europol. Canadian participants included the Royal Canadian Mounted Police and Ottawa Police Service.
The Justice Department also credited technical assistance from ICHIP The Hague, Fraunhofer FKIE, Registrar of Last Resort, OpenAI and Sharktech.
Senior Counsel Thomas Dougherty of the department’s Computer Crime and Intellectual Property Section and Assistant U.S. Attorney Jasand Mock of Colorado are prosecuting the case. The department’s Office of International Affairs assisted.
The release did not announce arrests, identify Gootloader’s operators or specify how many U.S. domain names authorities seized.